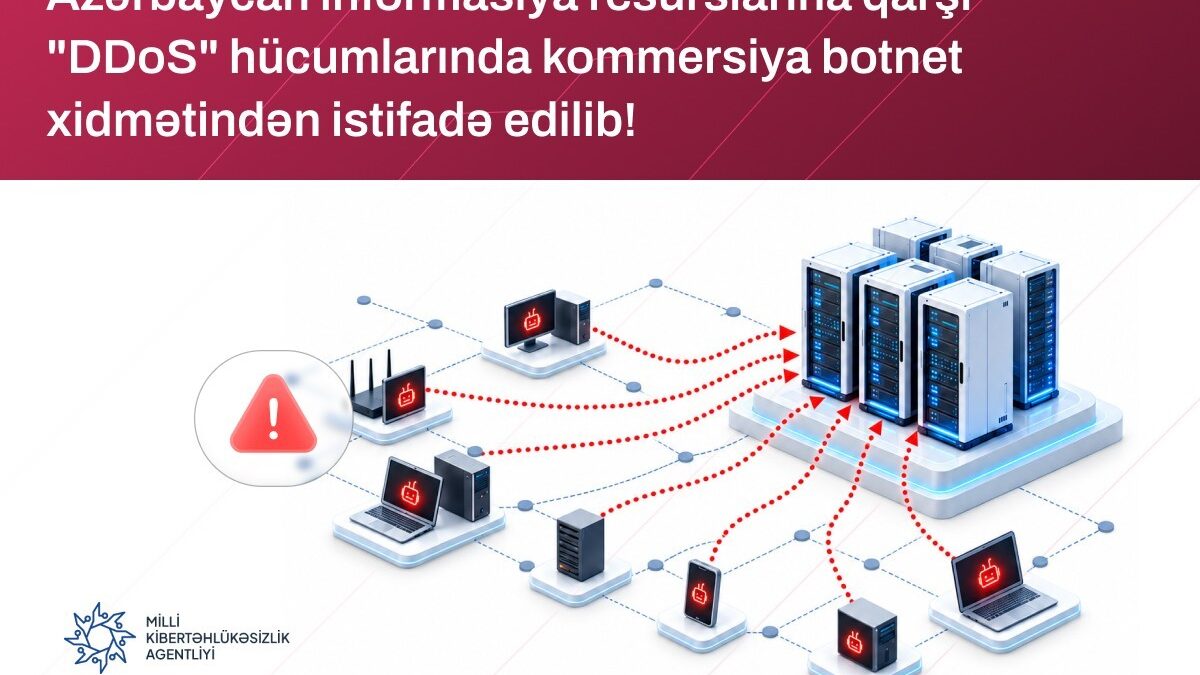
Distributed Denial of Service (DDoS) attacks were carried out against Azerbaijani information resources between October 13-15, 2026.
According to information provided to elchi from the National Cybersecurity Agency, the hacktivist group “313 Team,” operating on the “Telegram” platform, claimed responsibility for the attacks. During the attacks, information resources of government agencies, media organizations, Azerbaijani diplomatic missions abroad, and other organizations were targeted.
Technical investigations conducted by the National CERT revealed that a commercial DDoS service known as “Litterbox” (also known as “Catbox”) was used in carrying out the attacks. This service is offered through “Telegram” channels, and payments are accepted in cryptocurrency.
The service enables the execution of attacks aimed at disrupting the accessibility of target resources by generating intensive traffic over various network protocols such as GRE, ICMP, UDP, and TCP.
The use of commercial botnet services is one of the factors facilitating the organization of DDoS attacks. Such services expand the technical capabilities of attacks, creating additional cybersecurity risks for the information resources of various organizations.
During the investigation, it was also determined that the service allows for the redirection of attack traffic through bots located in pre-selected countries. This feature can reduce the effectiveness of defense measures based on the geographical origin of the attack traffic.
Measures are being continued by the National CERT to investigate similar cyber threats, strengthen the protection of information resources, and mitigate the impact of potential incidents. Indicators of compromise related to the investigated attack campaign have been added to the Incident Information Exchange Platform (misp.cert.az) actively used by the Agency.
Relevant organizations are advised to increase the resilience of their information resources, continuously monitor network traffic, and strengthen protection mechanisms against DDoS attacks.